安心・安全なNONOSウォレット
Trezorエコシステムで、NONOS資産を完全に安心して管理できます。
- ハードウェア・ウォレットで保護
- 互換性のあるホットウォレットと使う
- 200万人以上のお客様に信頼されています
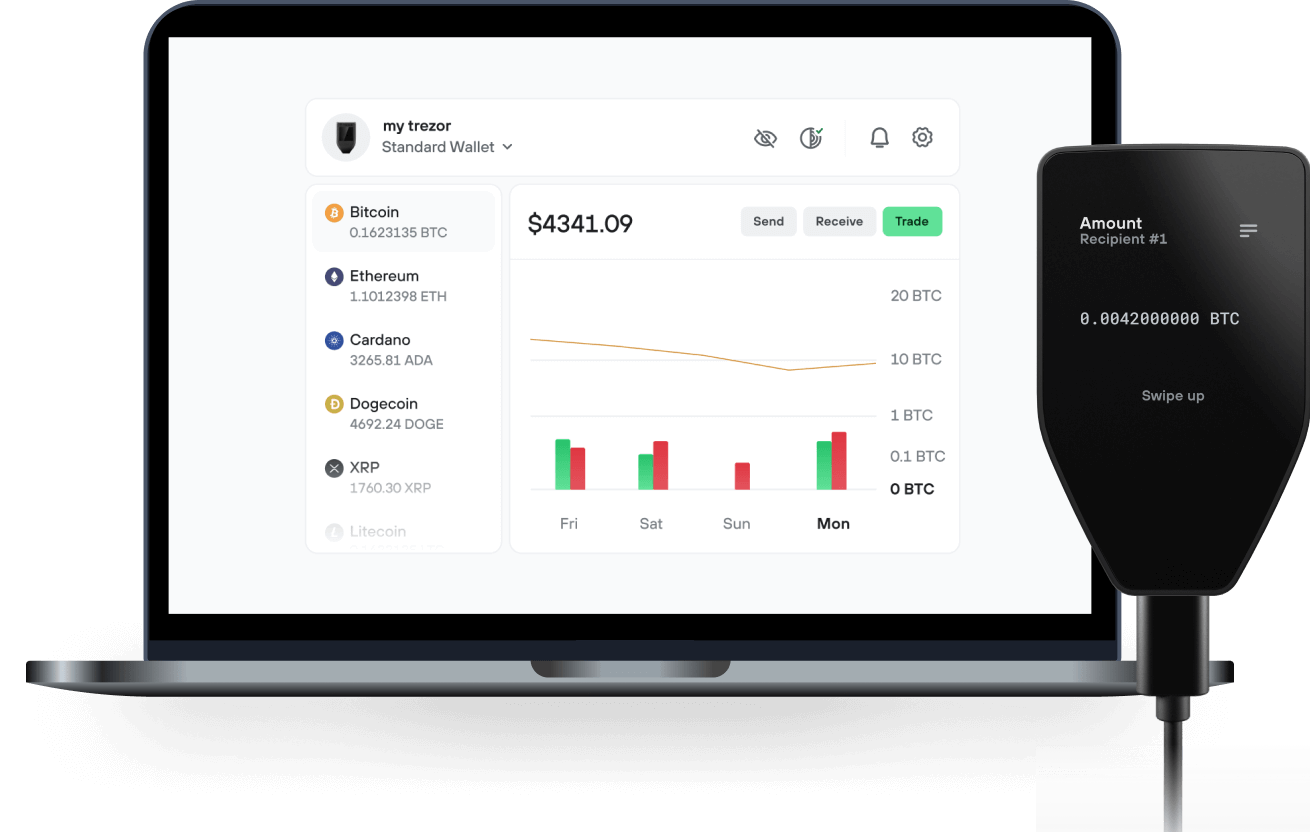
NONOSをTrezor Suiteアプリでで送信、受信

送信&受信
NONOSをサポートするTrezorハードウェア・ウォレット
Trezorをウォレットアプリと同期
NONOSを、複数のウォレットアプリと同期させたTrezorハードウェア・ウォレットで管理しましょう。
Trezor Suite
MetaMask
Rabby
対応 NONOS ネットワーク
なぜハードウェア・ウォレットを使うのですか?
Trezorでオフライン管理
- コインは100%あなたのものです
- あなたのウォレットはオフラインで100%安全です
- お客様のデータは100%匿名です
- あなたのコインはどの会社にも紐付いていません
オンライン取引所
- 取引所が破綻すると、コインを失うことになります
- 取引所はハッカーの標的
- あなたの個人データが漏洩する可能性があります
- コインを、あなたはまだ完全に自分のものにしていません。
TrezorでNOXを使う方法
Trezorを接続
サードパーティ製のウォレットアプリを開く
資産を管理しましょう
お手持ちのNOXを最大限に活用しよう
TrezorはあなたのNOXを安全に保護します
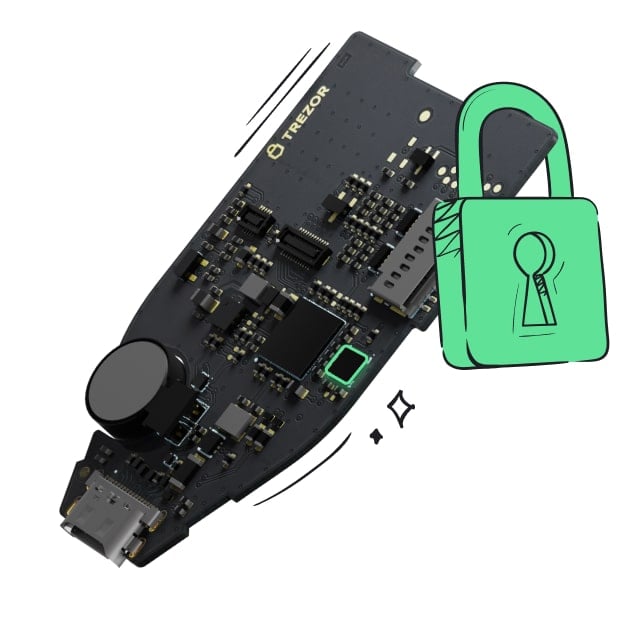 セキュア・エレメントにより保護されています
オンラインとオフライン、両方の脅威に対する最強の防御
 あなたのトークン、あなたの管理
デバイス上での承認により、すべてのトランザクションを完全に制御
 セキュリティシールが、梱包やTrezorハードウェア・ウォレットに改ざんがないことを保証します。
透明なウォレットデザインが、あなたのTrezorをより優れた、より安全なものにします。
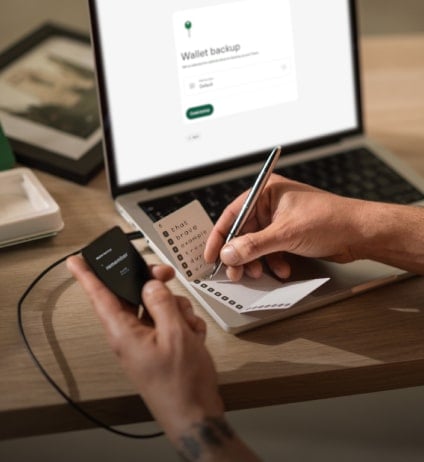 シンプルでわかりやすいウォレット・バックアップ
新しいバックアップ規格でデジタル資産へのアクセスを取り戻しましょう
 初日からの安心を
パッケージとデバイスのセキュリティ・シールでTrezorの完全性を守ります
NØNOS is an operating system built around privacy at the level of the kernel. Its design position is that a program is owed nothing and receives only what it has been explicitly granted.
The kernel is a microkernel with capability-based security. The component that grants and checks authority is under four thousand lines and is formally verified: the Rust is translated into Lean 4 by Charon and Aeneas, and the model is machine-checked to refine the extracted code, so the theorem covers the capability system as it ships.
Every program runs as a capsule, signed and started with exactly the permissions declared in its manifest, checked at spawn against the ceiling carried in its certificate. A capsule granted no network capability has no route to the network, no interface through which to request one, and no consent dialog through which a user can be persuaded to provide one. There is no root account and no administrator, so there is no authority to escalate toward.
Device drivers, the TCP/IP stack, the display server, the browser and the wallet/apps all run as capsules outside the kernel. Roughly 600k + lines of the system hold no privilege and have no path into the kernel address space.
The system is RAM-resident. After shutdown no logs, caches, browsing history or device identity remain on the machine. Network traffic leaves through an onion mixnet implemented inside the kernel with a fresh key agreement at every hop. Nothing executes unproved. The bootloader verifies the kernel under two independent signature schemes, one of them post-quantum, then checks the kernel own STARK proof against a root compiled into the bootloader. Each capsules proof is verified before its image is mapped, and a missing or invalid proof means the capsule does not run. The proving system is the project own transparent STARK over the Goldilocks field, requiring no trusted setup and no pairing-based cryptography. That same prover settles NOX Shield, a private transfer protocol verified on Ethereum by a Solidity contract. NOX is the ecosystem ERC-20 token on Ethereum.