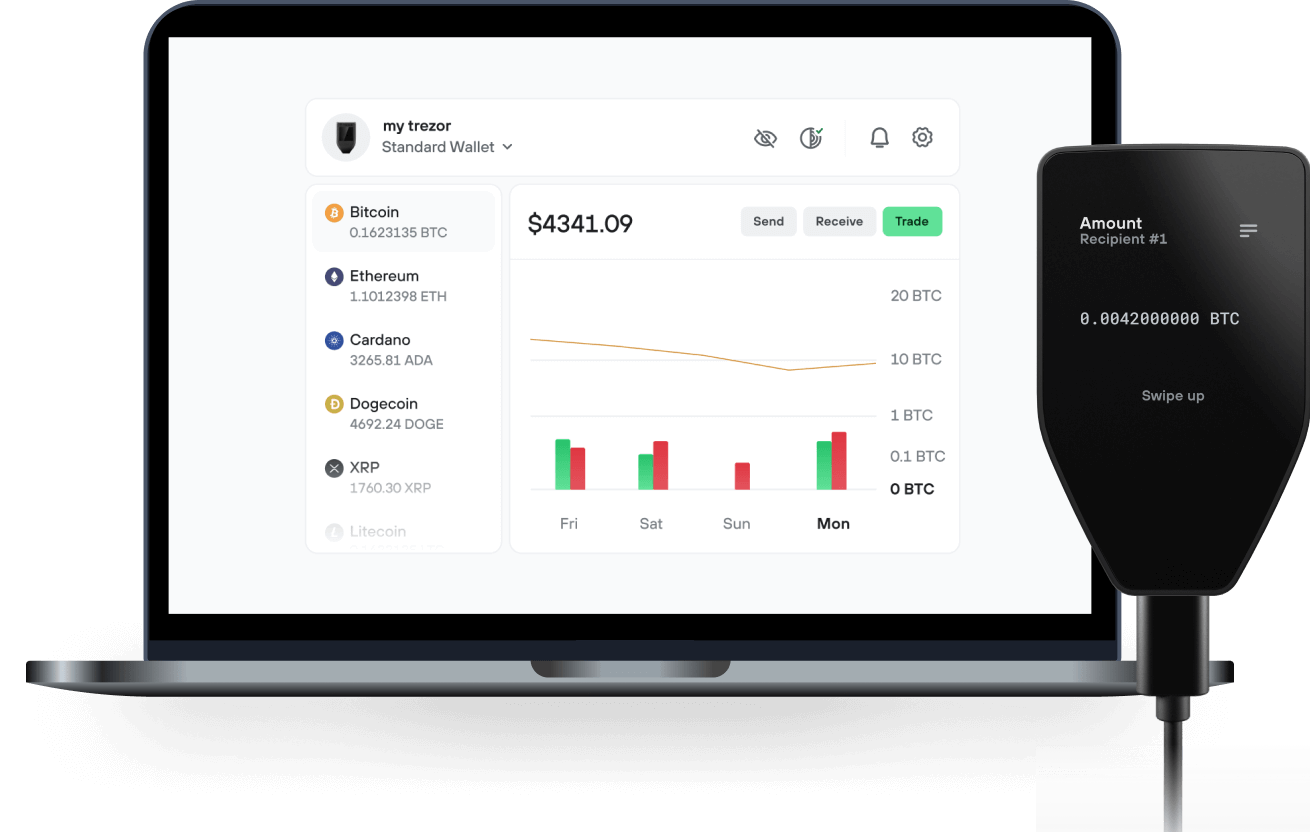
收发您的 NONOS 通过 Trezor Suite 应用

收发
支持 NONOS 的 Trezor 硬件钱包
让您的 Trezor 同步至钱包应用
通过将 Trezor 硬件钱包与多个钱包应用同步,管理您的 NONOS。
Trezor Suite
MetaMask
Rabby
支持的NONOS网络
为什么要用硬件钱包?
离线安全保护,尽在 Trezor
- 您 100% 拥有您的加密货币
- 离线保护私钥,大幅降低在线攻击风险
- 您的数据 100% 匿名
- 您的加密货币不受任何公司控制
在线交易所
- 若交易所出现问题,您将失去加密货币
- 交易所是黑客攻击的目标
- 您的个人数据可能会被暴露
- 您并不真正拥有您的加密货币
如何在 Trezor 上使用NOX
请连接您的 Trezor 设备
打开第三方钱包应用
管理您的资产
充分利用您的 NOX
Trezor 助您安心管理 NOX
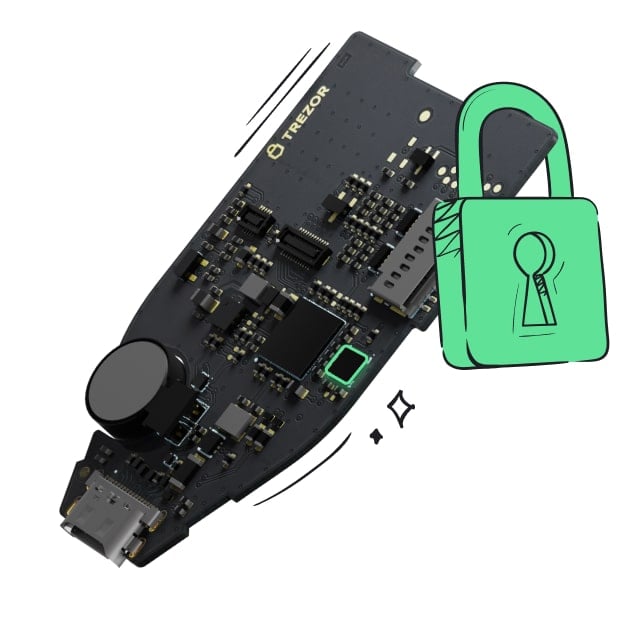 受安全芯片保护
对抗在线与离线威胁的可靠防线
 您的代币,您做主
通过设备确认,全面掌控每笔交易
 安全始于开源
透明钱包设计让您的 Trezor 更优更安全
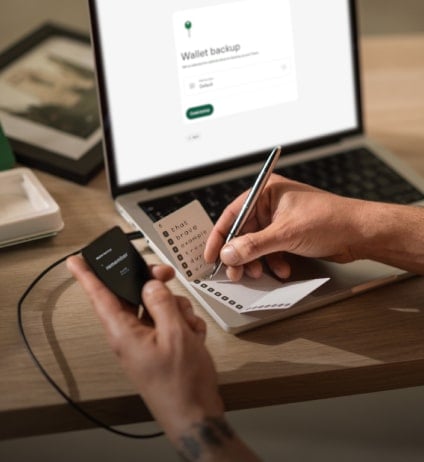 清晰简单的钱包备份
借助新一代备份标准恢复数字资产
 从第一天起就信心十足
包装与设备防拆封条共同保障 Trezor 设备完整性
NØNOS is an operating system built around privacy at the level of the kernel. Its design position is that a program is owed nothing and receives only what it has been explicitly granted.
The kernel is a microkernel with capability-based security. The component that grants and checks authority is under four thousand lines and is formally verified: the Rust is translated into Lean 4 by Charon and Aeneas, and the model is machine-checked to refine the extracted code, so the theorem covers the capability system as it ships.
Every program runs as a capsule, signed and started with exactly the permissions declared in its manifest, checked at spawn against the ceiling carried in its certificate. A capsule granted no network capability has no route to the network, no interface through which to request one, and no consent dialog through which a user can be persuaded to provide one. There is no root account and no administrator, so there is no authority to escalate toward.
Device drivers, the TCP/IP stack, the display server, the browser and the wallet/apps all run as capsules outside the kernel. Roughly 600k + lines of the system hold no privilege and have no path into the kernel address space.
The system is RAM-resident. After shutdown no logs, caches, browsing history or device identity remain on the machine. Network traffic leaves through an onion mixnet implemented inside the kernel with a fresh key agreement at every hop. Nothing executes unproved. The bootloader verifies the kernel under two independent signature schemes, one of them post-quantum, then checks the kernel own STARK proof against a root compiled into the bootloader. Each capsules proof is verified before its image is mapped, and a missing or invalid proof means the capsule does not run. The proving system is the project own transparent STARK over the Goldilocks field, requiring no trusted setup and no pairing-based cryptography. That same prover settles NOX Shield, a private transfer protocol verified on Ethereum by a Solidity contract. NOX is the ecosystem ERC-20 token on Ethereum.